ASOS app users notified by hackers about personal data breach
Published: 06/10/2026
| Last Updated: 08/10/2026
| BBC News
UK-based fashion retailer ASOS is investigating a supply-chain-related cyberattack involving unauthorised access to its online app after thousands of shoppers received a notification claiming hackers had fully compromised its systems. The retailer confirmed that a third party may have accessed basic personal information, including customer names and contact details. However, it stated that payment card details and passwords were not compromised, and operations across its website and app continue without disruption.
The notification directed users to the Telegram messaging platform, where the threat actors identifying themselves as the Xuanye Group claimed to have fully compromised the company's Snowflake instance, a cloud service used for data processing and push notifications. The group stated that it is holding customer information on its servers. Asos, which has taken out cybersecurity and business continuity insurance, restricted access to the notification platforms, engaged specialist advisers, and received support from the National Cyber Security Centre (NCSC).
The incident caused Asos shares on the London Stock Exchange to fall more than 14% before recovering to an 11% decline.
In an update on Thursday, ASOS confirmed that hackers are in possession of the names, addresses, phone numbers, emails and customer numbers of millions of its online customers. Details of what customers search for on the company's website have also been stolen, which the company warned could be used to target phishing scams.
ASOS also explained that the breach occurred after the hacking group gained access to an employee account "by impersonating a trusted contact to obtain log in credentials."
In a statement to affected ASOS customers on Wednesday, Paul Arnold MBE, CEO of the Information Commission (ICO), said: "We understand how unsettling it can be to receive a message from apparent hackers claiming to have access to your personal information. It's not the sort of message anyone expects to receive, and it can understandably leave people concerned about what information may have been exposed and what they should do next.
We would encourage anyone who receives a message of this nature to stay alert. Be cautious of any links or attachments, and do not click on links in unexpected texts or emails claiming to relate to your account. If you want to change your password, log in to your account directly through the official website or app and update it in the usual way. Monitor bank accounts and online services for unusual activity, and never share personal or financial information in response to unexpected contact.
More broadly, using strong, unique passwords and enabling multi-factor authentication can help keep accounts secure. Anyone concerned about their personal information can find practical advice and support on our website."
Training Announcement: The BCS Practitioner Certificate in Information Risk Management (PCIRM) is an advanced-level programme for data specialists who actively monitor and minimise the risk of cyberattacks, information security incidents, and data protection violations. Find out more.

Information Risk Training
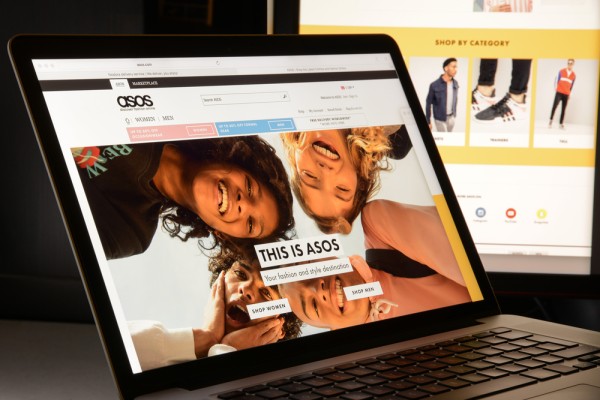
Image from Shutterstock, credit Casimiro PT
Information Risk Training
What is this page?
You are reading a summary article on the Privacy Newsfeed, a free resource for DPOs and other professionals with privacy or data protection responsibilities helping them stay informed of industry news all in one place. The information here is a brief snippet relating to a single piece of original content or several articles about a common topic or thread. The main contributor is listed in the top left-hand corner, just beneath the article title.
The Privacy Newsfeed monitors over 300 global publications, of which more than 3,250 summary articles have been posted to the online archive dating back to the beginning of 2020. A weekly roundup is available by email every Friday.